Sekura – Cyber Security WordPress Theme
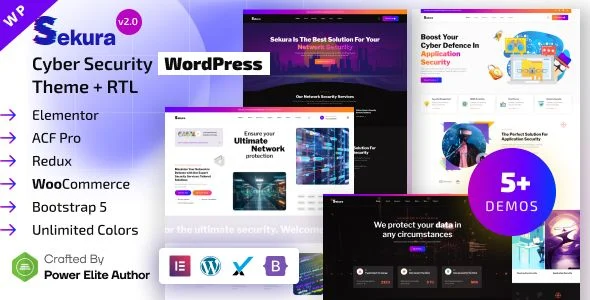
Sekura: Technical Overview & Architecture
Sekura – Cyber Security WordPress Theme is a WordPress theme engineered for cybersecurity consultancies, managed IT service providers, and security analysts who need a hardened, conversion-oriented web presence. Its template hierarchy is compiled with a minimized DOM depth, keeping nested container levels low so that service pages carrying dense pricing tables, vulnerability-report grids, and case-study cards render without layout thrash. UI state updates run through asynchronous AJAX cycles on the options panel and contact forms, refreshing form validation messages and portfolio filters in the browser without triggering full page reloads. Under the hood, the theme registers its assets through WordPress enqueue hooks, loading minified CSS and deferred JavaScript only on templates that require them.
Page assembly is handled through native Elementor integration: every demo section ships as an editable widget block, so a services page can be reordered, cloned, or restyled directly inside the Elementor editor without touching template files. A centralized administrative panel exposes more than four configuration groups, including global color scheme overrides for the dark and light palettes, typography stacks with per-heading-level font controls, header and footer layout variants, and sticky-navigation behavior toggles. Options persist through the WordPress Customizer API and theme mod storage, which means configuration survives core updates and can be exported with the site content.
Key Functional Features of the Sekura Theme
- Elementor Page Builder Integration: All demo layouts are reconstructed as editable Elementor sections, letting you modify hero banners, service grids, and CTA strips through drag-and-drop widgets while the underlying PHP templates remain untouched.
- WooCommerce Compatibility: Full template override support for product archives, single-product views, and checkout pages allows penetration-testing packages and audit services to be sold as purchasable products with standard cart and payment flows.
- Responsive & Retina-Ready Rendering: Media queries are applied at multiple breakpoints with vector icons and 2x image support, keeping service icons and logo assets crisp on high-density mobile displays.
- SEO-Friendly Markup Structure: Semantic HTML5 tags, schema-ready heading hierarchies, and clean permalink handling give crawlers a parseable document structure that supports long-tail ranking for security service queries.
- Translation-Ready & WPML Compatible: All strings are wrapped in localization functions with bundled .pot files, enabling multilingual deployments for firms serving clients across multiple regions.
- Performance-Optimized Codebase: Conditional asset loading, minified stylesheets, and lazy-loaded imagery keep requests per page low, which directly supports passing Core Web Vitals thresholds on shared hosting.
Production Deployment & Use-Case Scenarios
- Cybersecurity Consultancy Site: A consultancy publishes service categories such as penetration testing, compliance auditing, and incident response as dedicated Elementor pages, then routes visitors into an AJAX contact flow for scheduling assessments.
- Managed IT & SaaS Provider Platform: Subscription tiers for monitoring and endpoint protection are configured as WooCommerce products with tiered pricing tables, turning the site into a functioning sales channel for recurring service plans.
- Security Research & Analyst Blog: An independent analyst or research team runs a content hub with categorized threat-analysis posts, newsletter capture modules, and author profiles, building a readership around disclosure reports and industry commentary.
Technical Architecture & Compatibility Standards
The theme targets WordPress 6.x running on PHP 8.0 or higher, following current WordPress coding standards for escaping, sanitization, and nonce verification on all front-end forms. Cross-browser testing covers recent versions of Chrome, Firefox, and Safari, with Flexbox and Grid layouts applied without legacy float fallbacks that bloat the stylesheet. Core Web Vitals budgets are addressed through deferred script execution, responsive image markup with srcset, and a lightweight icon system that avoids heavy icon-font payloads.
Interoperability extends beyond the page builder: the theme coexists with standard caching plugins, SEO plugins, and multilingual stacks including WPML, because template output is filter-driven rather than hard-coded. Custom post types for services, case studies, and team members are registered with clean rewrite slugs, so permalinks remain stable when the site structure changes or when content is migrated between staging and production environments.
Frequently Asked Questions
Does Sekura support Elementor for full page customization?
Yes, every demo page is built with editable Elementor sections, and all widgets can be reordered or restyled without modifying PHP template files.
Can I sell cybersecurity services directly through the theme?
Yes, the theme is fully WooCommerce-compatible, so audit packages, monitoring subscriptions, and consulting retainers can be sold as products with standard checkout flows.
Does Sekura require paid third-party plugins to function?
No, the core demo layouts, customization panel, and post types operate on the bundled page builder setup without additional premium plugin purchases.
Is the theme suitable for a multilingual security firm website?
Yes, all interface strings are translation-ready with bundled .pot files, and the templates are WPML-compatible for deploying content in multiple languages.
Can the dark security aesthetic be adjusted for a lighter brand identity?
Yes, the centralized options panel exposes global color scheme controls, typography stacks, and header variants, allowing the default dark palette to be replaced with a custom brand system.
-
1.9 LatestSeptember 20, 2026